

Integrating SAP application logs with SIEM platforms is hard because of log complexity, volume, maintenance and missing IP data. The Cybersecurity Extension for SAP Solution Manager overcomes these obstacles by filtering, normalizing and enriching SAP security event data.
Executive Summary
Security Information and Event Management (SIEM) platforms collect log data from applications, hosts, routers, switches, firewalls and other endpoints and analyze events in real time. They deliver full benefits only with complete coverage, which includes SAP application logs. Integrating those logs directly is difficult for four reasons: the logs are numerous and have no standard format, raw log volume can reach gigabytes and terabytes, the many integration points are costly to maintain, and SAP logs often lack source and destination IP addresses for cross-platform correlation. The Cybersecurity Extension for SAP Solution Manager addresses these obstacles. Its Monitoring and Alerting Infrastructure (MAI) monitors logs at source, so event logs are not extracted and replicated to external repositories. Alerts are normalized into a standardized structure, enriched with source and destination IP addresses, and written to a daily event file that SIEM platforms ingest through a single point of integration. The benefits are lower costs, rapid deployment, ease of maintenance and enriched event data for cross-platform correlation. The example uses Splunk Enterprise, and the approach also works with QRadar, ArcSight and Log Rhythm.
Key Takeaways
- SIEM platforms need complete coverage, including SAP application logs, to deliver full benefits.
- Direct SAP-to-SIEM integration is hard because of log complexity, volume, maintenance and missing IP data.
- The Monitoring and Alerting Infrastructure (MAI) in Solution Manager monitors logs at source, reducing bandwidth and storage needs.
- Alerts are normalized, enriched with source and destination IPs, and written to a daily event file for SIEM ingestion.
- The approach works with Splunk Enterprise, QRadar, ArcSight and Log Rhythm.
What is a SIEM platform and why does it need SAP logs?
Security Information and Event Management (SIEM) platforms combine the ability to collect log data from applications, hosts, routers, switches, firewalls and other endpoints with the ability to analyze events in real time. They support threat detection, event correlation and incident response with alerting and reporting capabilities.
SIEM platforms require complete coverage for maximum yield. Organizations reap the full benefits of SIEM platforms when monitoring logs throughout the technological infrastructure. This includes SAP application logs for organizations with SAP systems.
What are the challenges of integrating SAP logs with SIEM systems?
There are four main challenges: complexity, log volume, maintenance and missing correlation data.
Complexity. SAP systems typically contain multiple logs that capture security-relevant events. The SAP NetWeaver Application Server ABAP (AS ABAP) alone has at least seven such logs including the Security Audit Log, Gateway Server Log, HTTP Log, System Log, Transaction Log, Change Document Log, and the Read Access Log. The logs do not have a standardized format or structure. Some are captured at the file level and others are stored in SAP tables. The complexities involved in integrating multiple and distinct logs from each SAP system should not be underestimated, especially for large SAP landscapes.
Log volume. Raw event logs can grow to gigabytes and even terabytes within a relatively short period of time in SAP systems that often support thousands of end users and hundreds of cross-system connections. Transmitting large volumes of log data from SAP systems to SIEM platforms could consume high levels of network bandwidth. The need to store such data for analysis could also increase resource requirements and licensing costs for SIEM systems.
Maintenance. Monitoring and supporting the numerous integration points between SAP systems and SIEM platforms, as well as regular archiving to deal with the accumulation of log data, could lead to high maintenance costs.
Correlation. Many SAP logs do not natively include information to support cross-platform correlation using SIEM tools. This includes source and destination IPs for security events. Values for sources and destinations in SAP logs are often terminal names and SAP Systems IDs (SIDs) rather than IP addresses. Therefore, Security Operation Centers (SOCs) are not able to easily correlate SAP events with non-SAP events in SIEM platforms.
Challenges and how the Cybersecurity Extension addresses them
The following table compares each integration challenge with the capability that addresses it.
| Challenge | Problem with direct integration | How Solution Manager addresses it |
|---|---|---|
| Complexity | Multiple logs with no standardized format | Event data normalized using a standardized structure for all log sources |
| Log volume | Gigabytes to terabytes; high bandwidth and storage needs | Logs monitored at source, not extracted and replicated |
| Maintenance | Numerous integration points and archiving | Single point of integration for event data |
| Correlation | Terminal names and SIDs instead of IP addresses | Source and IP addresses included for each alert |
How does the Cybersecurity Extension for SAP Solution Manager monitor SAP logs?
The Monitoring and Alerting Infrastructure (MAI) in Solution Manager monitors logs at source without extracting and replicating event logs to external repositories. This reduces both bandwidth and storage requirements. MAI data providers support monitoring for all SAP logs including file and table logs in ABAP, HANA, and Java systems, and standalone components such as the SAProuter.
MAI periodically parses event logs using attack detection patterns configured in metrics. The frequency of metric checks is customizable and can range from every 60 seconds to several minutes apart. Intervals can be adjusted at the metric level which means metrics can have different monitoring intervals.
How are security alerts generated and enriched for the SIEM?
A pattern match triggers the MAI to generate alerts and email or SMS notifications for security events. Security alerts generated by Solution Manager are managed using applications such as Monitor Systems, System Monitoring and the Alert Inbox. Alerts can also be written to an external file by Solution Manager.
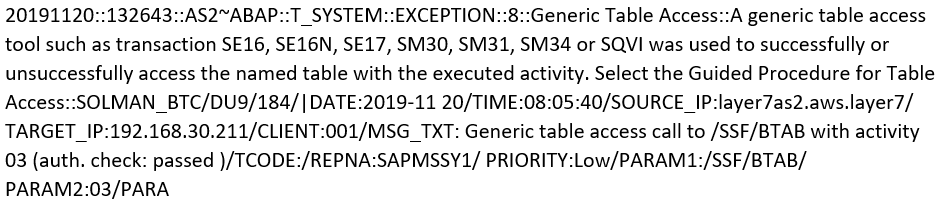
Solution Manager enriches event data by including source and IP addresses for each alert written to the file. This is intended to support correlation once the data is ingested by SIEM platforms. Event data is also normalized using a standardized structure for all log sources. The fields and separators for event details within each file are customizable and include values for alert name, description, date, time, system, system type, and event details. The event details can include information such as the event ID, username, source and destination IP addresses, and objects accessed by the user such as transactions, reports, function modules or URLs.
The example below includes <DATE>::<TIME>::<SYSTEM>::<MANAGED OBJECT TYPE>::<ALERT TYPE>::<PRIORITY>::<ALERT NAME>::<ALERT DESCRIPTION>::<ALERT DETAILS>. Each value is separated by ::
Can attackers remove traces of their actions from Solution Manager alerts?
Attackers cannot remove all traces of their malicious actions by modifying event logs alone, because event details are written to and stored within alerts in Solution Manager. They will also need to delete alerts and stop the triggering of email/SMS notifications of alerts in Solution Manager. This would be challenging since alerts cannot be deleted in Solution Manager. They can only be confirmed. All alerts are retained and only removed by periodic housekeeping jobs designed to delete aged alerts.
How do event files reach the SIEM platform?
Event files can be stored on the Solution Manager host or an external host or file server. A new event file is created by Solution Manager for each day. The contents of the newest file can be periodically pushed to SIEM platforms or pulled by SIEM systems directly from relevant directories. Since there is a single point of integration for event data between SAP and SIEM systems, maintenance efforts are relatively low.
What are the benefits of integrating SAP events with SIEM using the Cybersecurity Extension?
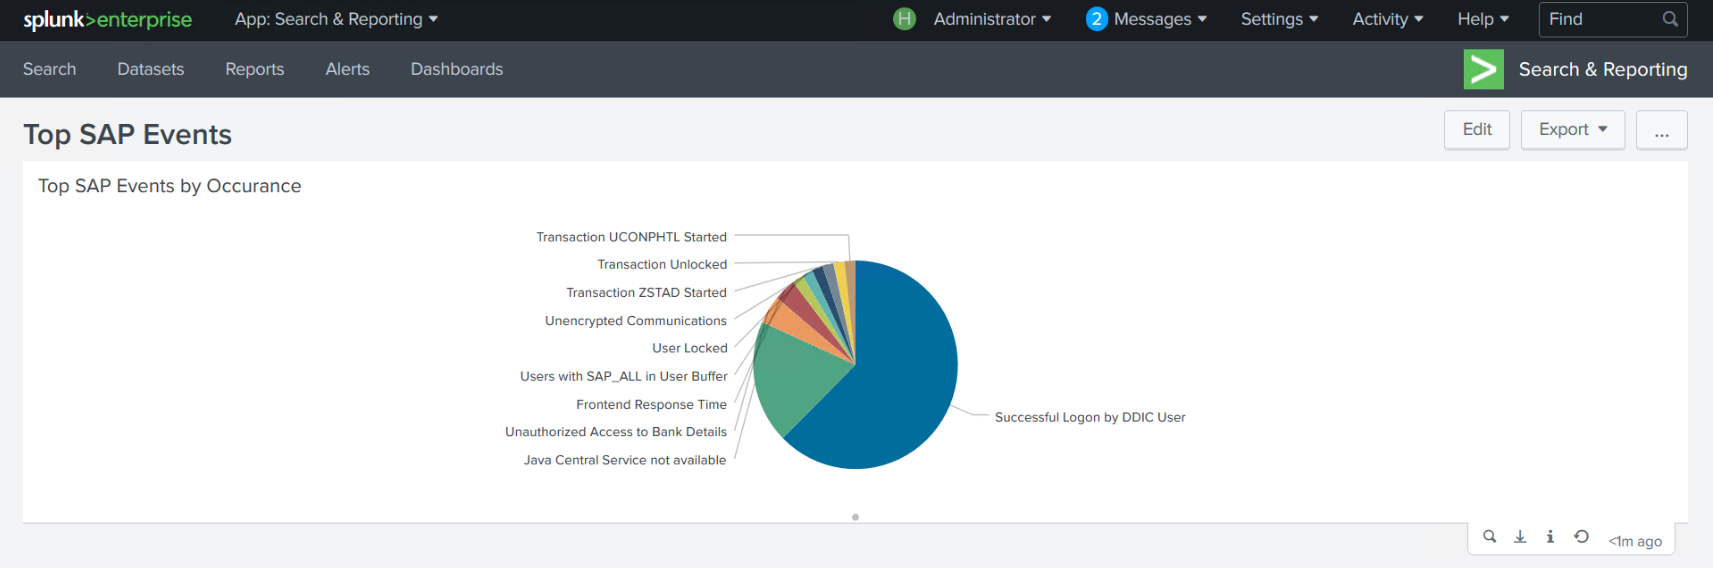
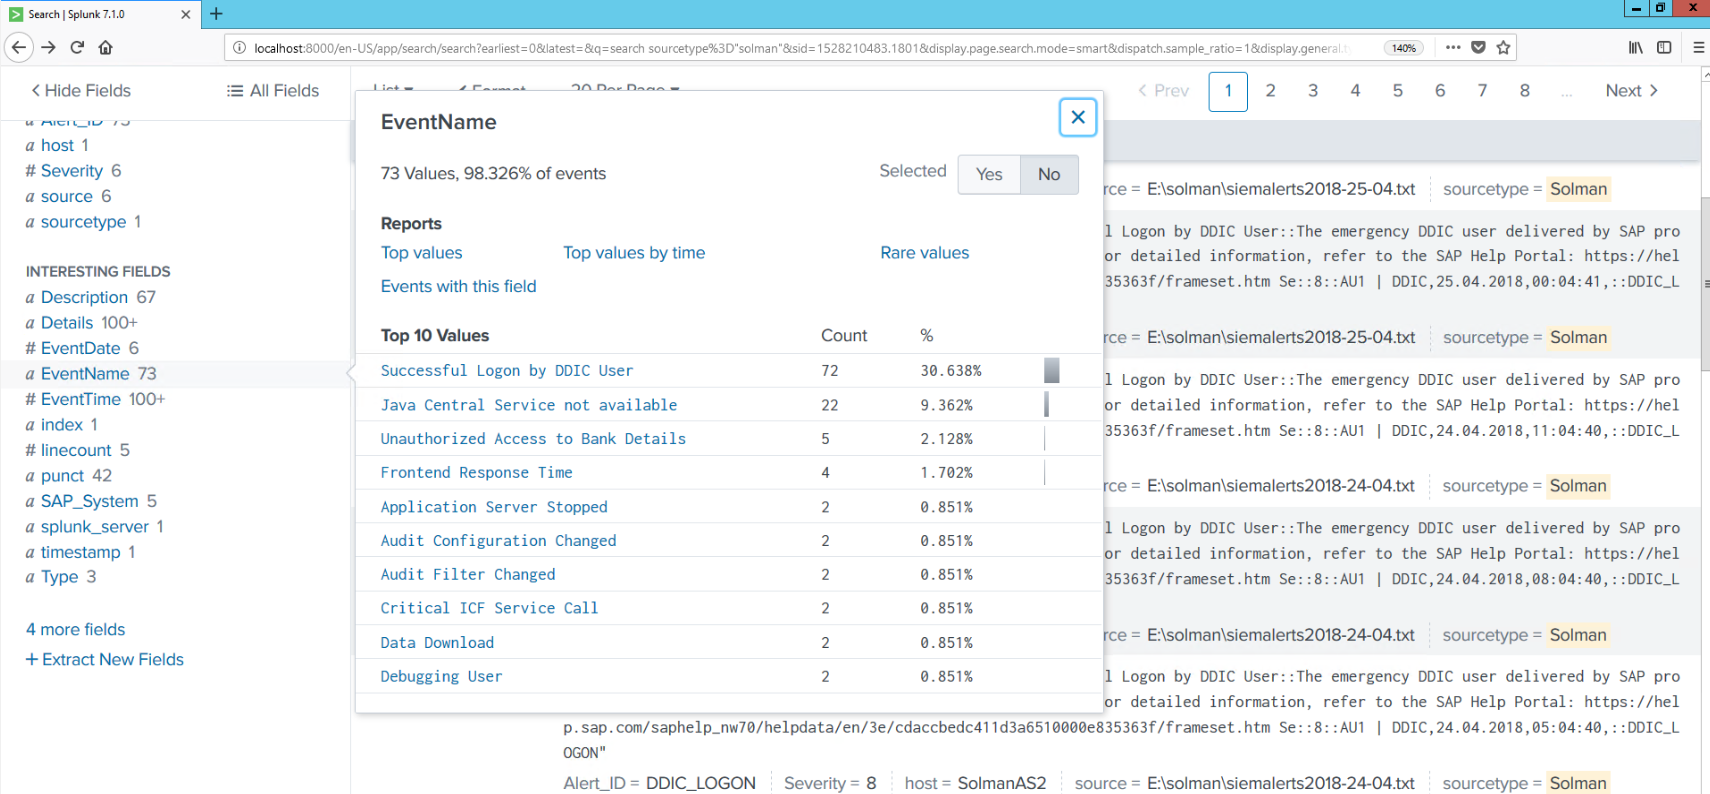
The benefits include lower costs, rapid deployment, ease of maintenance, and the enrichment of event data to support cross-platform correlation. The example below is for SIEM integration with Solution Manager for Splunk Enterprise. However, the approach can also be used to integrate security event data with other SIEM systems including QRadar, ArcSight and Log Rhythm.
Frequently Asked Questions
Why is it difficult to integrate SAP logs with a SIEM?
SAP systems have many security logs with no standardized format, raw volumes that can reach gigabytes or terabytes, numerous integration points to maintain, and sources and destinations recorded as terminal names and SIDs rather than IP addresses.
How does Solution Manager reduce bandwidth and storage needs?
The Monitoring and Alerting Infrastructure (MAI) in Solution Manager monitors logs at source without extracting and replicating event logs to external repositories. This reduces both bandwidth and storage requirements for the SIEM integration.
What data do Solution Manager event files contain?
Fields and separators are customizable and include alert name, description, date, time, system, system type, and event details. Event details can include the event ID, username, source and destination IP addresses, and objects accessed such as transactions, reports, function modules or URLs.
Which SIEM platforms can the approach integrate with?
The example integrates Solution Manager with Splunk Enterprise. The approach can also be used to integrate security event data with other SIEM systems including QRadar, ArcSight and Log Rhythm.