

Custom SAPUI5 applications are a core component of modern SAP environments, but they lack the native security patching provided by SAP, making them prime targets for attackers. To secure these applications, organizations must implement automated static source code scanning to identify and remediate vulnerabilities throughout the development lifecycle.
Why is custom SAPUI5 application security critical?
SAPUI5 is the foundation for Fiori applications in SAP S/4HANA and SAP HANA, providing a flexible framework that integrates with ABAP programs via OData services. Because SAPUI5 applications generate their own JavaScript and handle HTML rendering, they are significantly more susceptible to code-level vulnerabilities than traditional Web Dynpro applications. Since these custom applications are not maintained or patched by SAP, the responsibility for identifying vulnerabilities and preventing misuse rests entirely with the customer.
How does the Cybersecurity Extension for SAP (CES) protect UI5 apps?
The Cybersecurity Extension for SAP (CES) automates static source code scanning to detect over 900 distinct vulnerabilities in custom SAPUI5 applications. By integrating this scanning process into the development lifecycle, organizations can ensure their custom code meets stringent security standards before deployment. CES identifies critical security flaws, including:
- Code injection
- SQL injection
- Cross-site scripting (XSS)
- Directory traversal
- Insufficient authentication or authorization checks
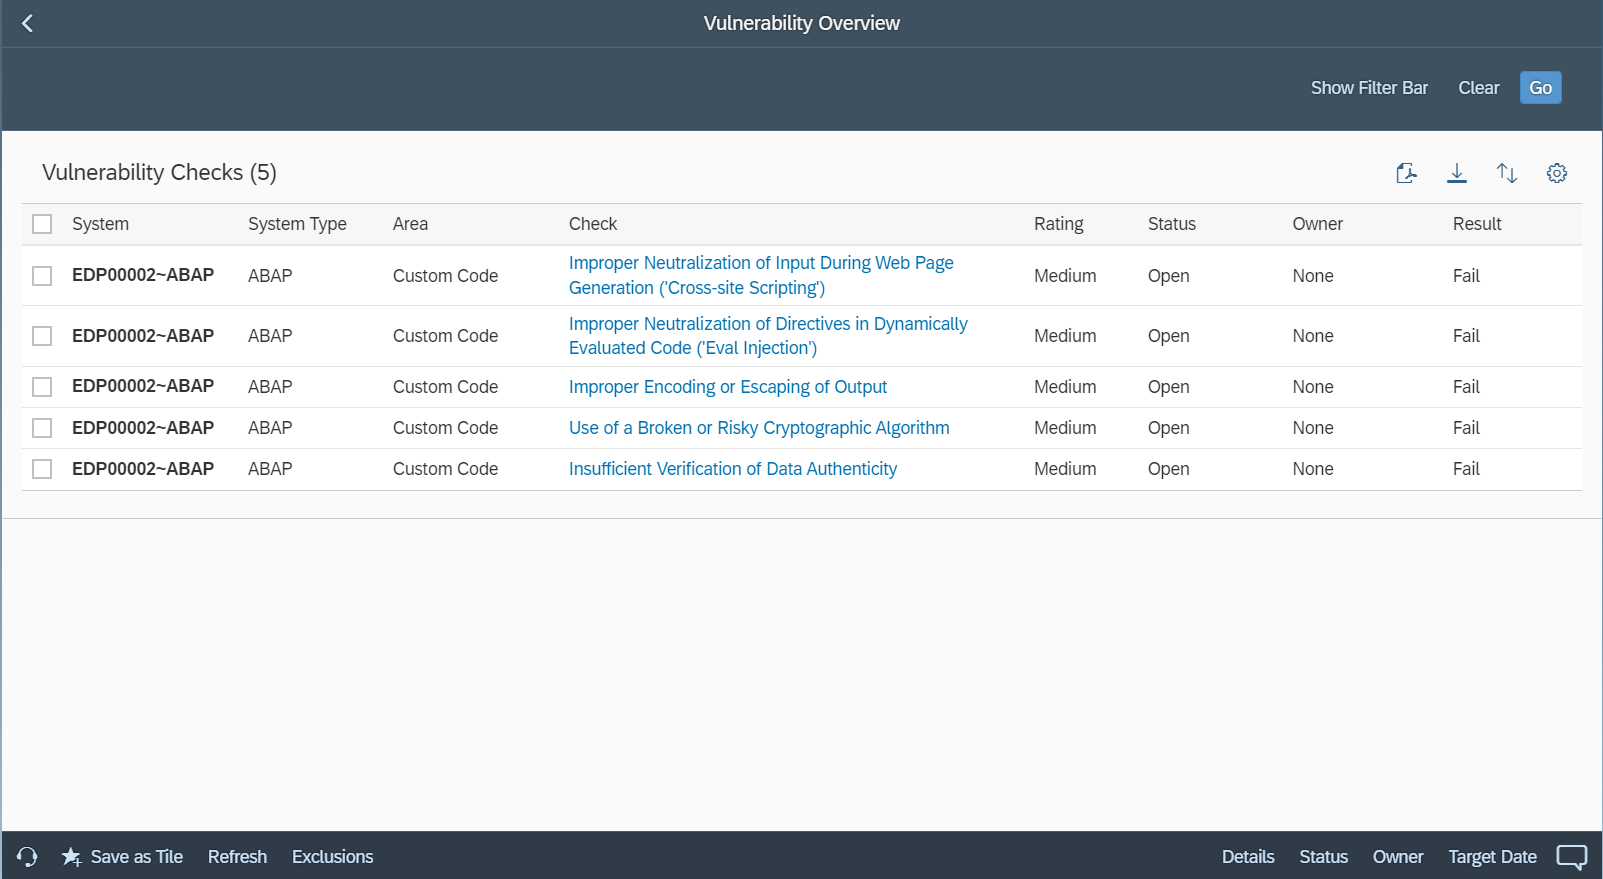
What insights does the Cybersecurity Extension for SAP provide?
CES provides actionable intelligence for each detected vulnerability, enabling developers to remediate issues efficiently. Each finding includes a comprehensive risk analysis, clear remediation guidance, and specific details regarding the impacted lines of code, objects, packages, and owners. Furthermore, findings are mapped to the Common Weakness Enumeration (CWE) framework, a software development standard supported by the U.S. Department of Homeland Security, to ensure ongoing compliance with industry best practices.
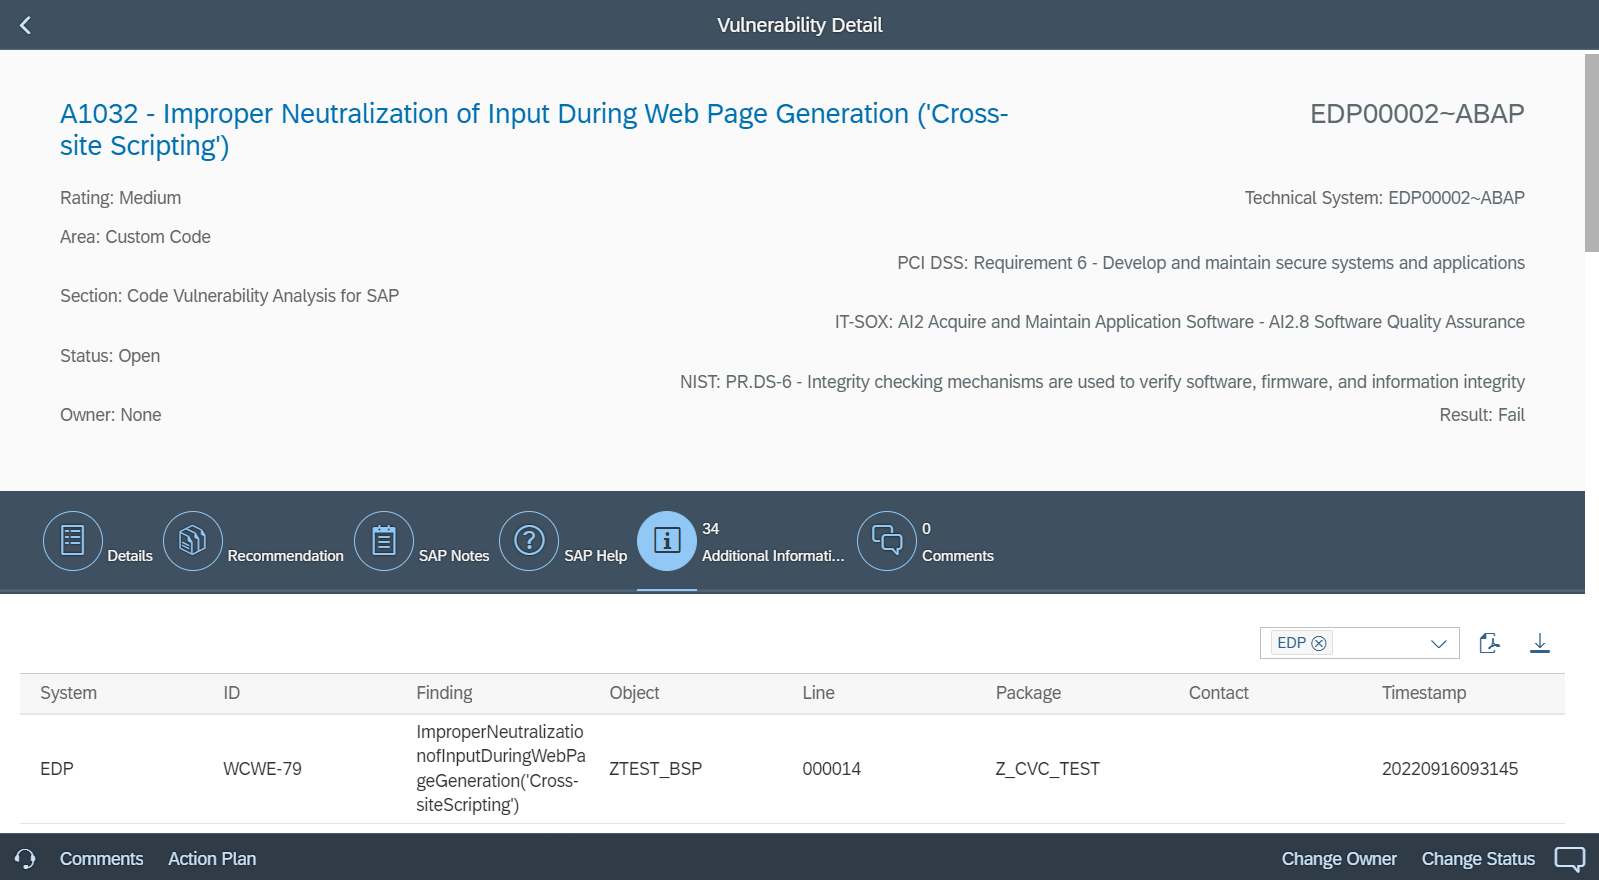
Vulnerability Management and Reporting
| Feature | Description |
|---|---|
| Analysis | Detects over 900 vulnerabilities in custom SAPUI5 code. |
| Management | Results are manageable via SAP Code Inspector (SCI). |
| Reporting | Export findings as Excel or PDF reports. |
| Integration | Integrated with the Vulnerability Report in the Fiori launchpad. |
Frequently Asked Questions
Why are custom SAPUI5 applications more vulnerable than other SAP code?
Custom SAPUI5 applications handle their own HTML rendering and JavaScript generation. Unlike standard SAP programs that receive security notes and patches, custom applications are not maintained by SAP, leaving the responsibility of security entirely to the customer.
What types of vulnerabilities does the Cybersecurity Extension for SAP detect?
The tool is designed to detect over 900 vulnerabilities, including high-risk issues like cross-site scripting (XSS), SQL injection, code injection, directory traversal, and failures in authentication or authorization logic.
How are scan results managed?
Results can be reviewed and managed directly within the SAP Code Inspector (SCI). Additionally, findings are integrated with the Vulnerability Report in the Cybersecurity Extension for SAP, which can be accessed via the Fiori launchpad for SAP Solution Manager, and exported for further analysis.